
Claude Code permission drift is how safe agent workflows become unsafe
Claude Code can start with a narrow task and end up with broad tool access. Treat permission changes like production changes: log them, review them, and tie them to rollback.
Claude Code can start with a narrow task and end up with broad tool access. Treat permission changes like production changes: log them, review them, and tie them to rollback.
The hardest CCAR-F distractors are often almost right. Learn to spot the architectural boundary they quietly cross.
CCAR-F study should train scenario judgment: what failed, which boundary was crossed, and which answer makes the agent architecture safer and more reliable.
My new Leanpub guide for the Claude Certified Architect Foundations exam is live. It focuses on scenario judgment, distractor analysis, practice exams, and the production architecture behind the badge.

Production AI agents need a revocation path before they get wider authority. If a Claude Code run, MCP tool, workflow agent, or RAG assistant goes wrong, the team should know exactly how to stop it.

Every new agent permission is a production change. Treat new MCP methods, data sources, write paths, credentials, and approval bypasses like releases with evidence and rollback.

Claude Code rollout and enterprise AI agent security need the same artifact: a control record that explains scope, authority, evidence, approval, and rollback.

Production AI agents need scoped authority, run evidence, approval gates, and rollback before the rollout expands. This is where Claude Code delivery work and enterprise agent security meet.

Production AI agents need more than good output. Before a team scales Claude Code or enterprise agents, the run must explain its task, tools, evidence, approval, and rollback path.
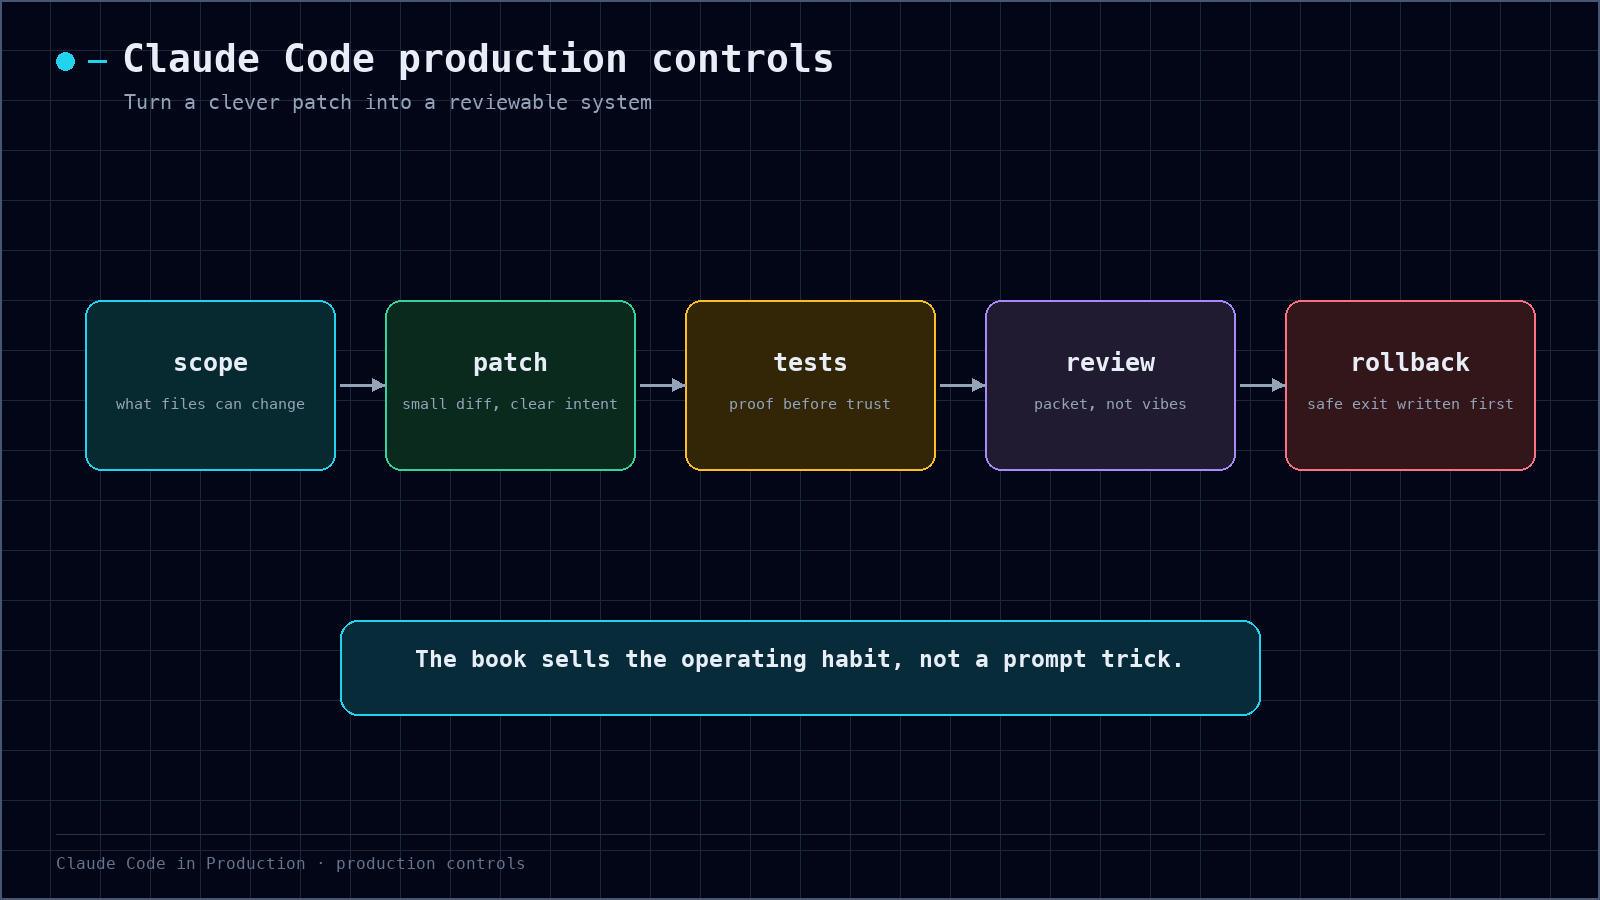
A clean Claude Code diff is not enough for production review. The reviewer needs the task contract, scope, commands, evidence, risks, rollback note, and approval record before merge.